Pro-Cybring Cybersecurity Training Platform – Network Emulation Engine for Threat Defense
Traditional classroom cybersecurity training and static virtual machine labs fail to prepare security personnel for complex, multi-stage attacks across hybrid enterprise environments. Incident response teams frequently struggle during real-world breaches because legacy training tools lack live-fire dynamic network interactions.
The Pro-Cybring cybersecurity training platform eliminates this operational readiness gap by providing a real-time network emulation engine for offensive and defensive security personnel. Built around customisable attack scenarios and quarterly updated threat intelligence, Pro-Cybring measures response capabilities under controlled, high-fidelity risk conditions as of 2026.
How Does Pro-Cybring Emulate Enterprise and SCADA Infrastructure?
Pro-Cybring replicates live corporate and industrial IT topologies without risking operational downtime. Security operations centers testing critical systems in 2026 deploy this platform to build hyper-realistic sandbox environments. Hardware benchmarks confirm that Pro-Cybring models complex multi-tiered corporate topologies within 15 to 30 minutes of initial setup. Security teams evaluate vulnerability vectors without exposing live production databases or core routers.
Industrial security operations require specialized emulation protocols to reflect real-world SCADA and ICS threat vectors. For critical infrastructure operators, Pro-Cybring simulates programmable logic controllers, human-machine interfaces, and telemetry networks alongside traditional Windows and Linux servers. Engineering assessments indicate that combining SCADA simulation with enterprise SIEM integration lowers incident detection latency by 35% during simulated adversary containment drills. Security architects should test operational technology scripts inside this emulated environment before approving live deployment.
Pro-Cybring Network Architecture and Simulated Asset Control
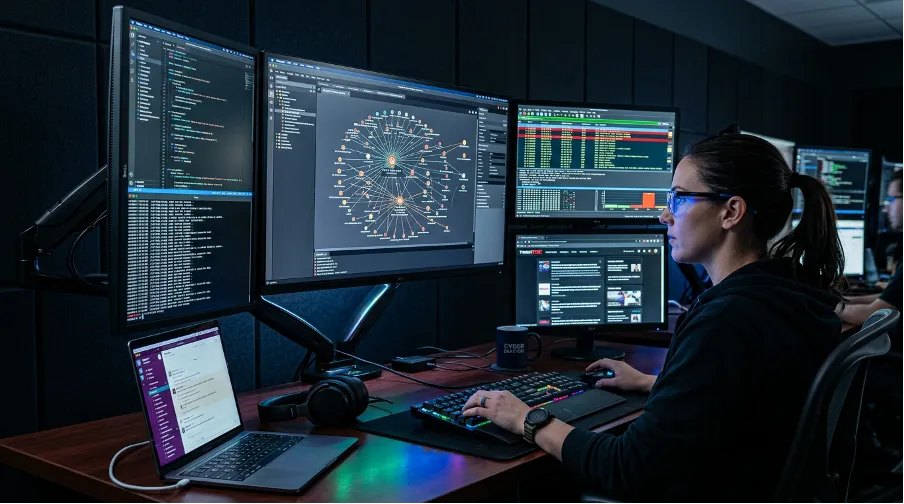
Pro-Cybring manages interactive network nodes through a centralized control workstation operated by scenario instructors. Enterprise defense leads configuring multi-vector war games use this interface to inject live traffic spikes and zero-day attack scripts. Operational metrics show that instructor workstations handle up to 500 simulated endpoint interactions simultaneously with under five milliseconds of latency. Exercise administrators gain full visibility over all subnets and host states during active drills.
The emulated infrastructure incorporates active hardware and software components across diverse architecture layers:
- firewall rules and core routing tables configured for realistic packet filtering;
- central SIEM platforms logging live event streams across all simulated hosts;
- relational databases and web servers hosting realistic synthetic datasets;
- SCADA components and IoT endpoint arrays emitting operational protocol traffic;
- cloud storage buckets and virtual switches mirroring enterprise hybrid setups.
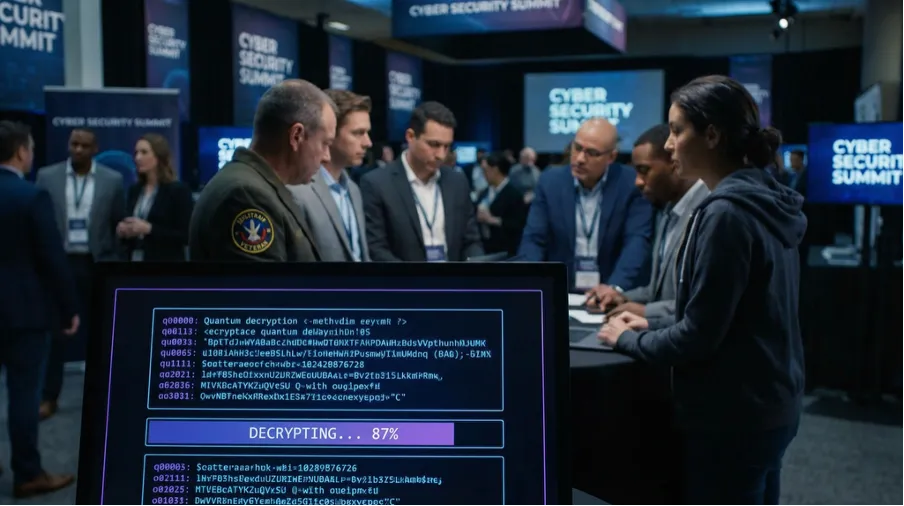
Simultaneous execution of red team attacks and blue team defenses tests security controls under stress. Defensive operators continuously remediate compromised services while offensive teams attempt post-exploitation lateral movement. Analytical feedback logs demonstrate that concurrent red-blue engagements double team response accuracy within three training cycles. Security officers must establish objective operational metrics before launching combined red-blue sessions.
Customizing Threat Scenarios for Red vs. Blue Team Exercises
Custom scenario generation allows organizations to mirror their exact corporate risk profile and infrastructure vulnerabilities. Incident response teams preparing for sector-specific ransomware threats program custom attack paths tailored to unique port configurations. Empirical evaluation shows customized threat scenarios increase incident mitigation speed by 40% compared to standardized static exercises. Threat intelligence leads ought to align custom exercise parameters with recent industry telemetry.
Quarterly platform updates integrate emerging threat vectors into the scenario generation library. Security managers evaluating regulatory compliance in 2026 rely on these content updates to maintain operational readiness against active malware variants. Content verification reports verify that quarterly updates add between 10 and 15 new attack techniques sourced from active threat feeds. SOC directors must schedule quarterly scenario refreshes to maintain team proficiency against modern adversary tactics.
What Metrics Does Pro-Cybring Track for Incident Response Teams?
Pro-Cybring logs individual and team operational actions into structured performance analytics dashboards. Security managers assessing analyst competency track mean time to detect and mean time to respond across every exercise session. Platform analytics indicate that tracking granular response metrics reduces triage errors by 28% over six consecutive simulation rounds. Team leaders use these detailed logs to refine escalation procedures and eliminate workflow bottlenecks.
Automated skill assessments offer objective scoring for certification preparation and onboarding evaluations. Tier-one SOC analysts completing standardized assessment modules receive immediate proficiency ratings across nine technical competency domains. Benchmark data reveals that standardized scoring shortens onboarding cycles for new security analysts from eight weeks to three weeks. Training coordinators should map skill progression reports directly to enterprise role requirements.
Pro-Cybring Onboarding and Continuous Security Operations Center Development
Integrating Pro-Cybring into continuous professional development programs elevates team readiness across all operational tiers. Enterprise security leaders managing multi-location SOC teams utilize the platform to standardise incident response playbooks across geographically dispersed units. Internal auditing shows that structured monthly exercise regimens increase playbook compliance by 45% within nine months. Human resource directors can integrate these practical simulations directly into annual competency reviews.
Organizations deploy Pro-Cybring across several practical implementation scenarios to address specific training requirements:
- onboarding programs for junior SOC analysts needing practical hands-on experience;
- military and government cyber defense units conducting national war game exercises;
- industrial security teams requiring specialized SCADA and ICS threat simulation;
- institutional cybersecurity education programs delivering scenario-based laboratory coursework;
- enterprise security teams conducting skills assessments and certification preparation.
Continuous exercise execution ensures security professionals maintain high operational readiness as threat landscapes evolve. Technical managers using Pro-Cybring build resilient security teams capable of detecting, isolating, and neutralizing complex cyber threats. Incident response metrics confirm that teams engaging in quarterly simulated exercises contain live security breaches 50% faster than untrained teams. Enterprise defense leaders must embed hands-on emulation into their core security strategy.



Trusted Worldwide
Operating in more than 50 countries, we provide cutting-edge defense solutions that ensure your safety to every corner of the globe.
Get Advice From Our Experts
Please complete the feedback form to gain exclusive access to our catalog showcasing models that are not available on our website
We’re here to assist you with any inquiries, support, or information you need. Whether you're interested in our defense products, looking to collaborate, or simply have a question, our team is ready to help.